This guide explains how to reduce online privacy risks while browsing adult-oriented content categories and third-party sites. Objectively, “P0rn0” is an obfuscated term commonly used in web discussions, often tied to adult material and higher tracking risk. We review key risk factors, practical safety steps, and conditions for safer browsing.
Many users search the internet for adult-oriented content categories using obfuscated terms like P0rn0. It’s understandable: people attempt to reduce moderation triggers, avoid keyword-based filtering, or keep search behavior from being flagged by certain platforms. But in practice, the bigger challenge is rarely “what content is shown”—it’s the ecosystem around the page that may come with that search trail: tracking scripts, redirect chains, credential-harvesting ads, privacy-invasive intermediaries, and data sharing by third parties that are difficult to see from the surface.
This article provides an objective, expert-style framework for understanding those risks and applying safer browsing practices. The goal is privacy protection, security hardening, and compliance-minded awareness when you encounter adult-oriented keywords or similar search behavior online. We focus on risk reduction and personal data protection—not on enabling access to illegal or harmful material.
To be explicit: we do not provide instructions to access illegal or harmful content. Instead, we discuss how to recognize and mitigate risk when you encounter adult-oriented keywords, obfuscated search terms, or related web pages that may have an elevated chance of intrusive tracking, deception, or scams.
P0rn0 is a leetspeak-style obfuscation of a widely recognized adult-related word. In many systems, obfuscation is used to bypass moderation filters, reduce keyword-based detection, or evade platform restrictions. A search query that includes obfuscated spellings often correlates with pages that are more likely to embed aggressive advertising, third-party trackers, questionable referral or landing flows, or permission baiting.
That said, the word itself is not the real threat. From an industry risk perspective, the main concern is the traffic environment and the typical delivery pattern: adult-oriented traffic has historically attracted different monetization strategies than general-interest browsing, including:
Because implementations vary by site, region, and ad network configuration, readers should treat any adult-oriented search trail as a higher-risk browsing context until safety settings are verified and the page’s behavior is understood.
When search terms like P0rn0 appear in a browsing path, you’re more likely to encounter specific technical and operational behaviors. The sections below provide an objective risk map you can use to decide what to harden, what to verify, and what to avoid. Think of this as a checklist of risk patterns—not as claims that every page is malicious.
Even when a page looks “simple” from the user interface, modern web delivery often includes trackers that collect information such as IP address (which can support rough geolocation), browser fingerprint signals, and behavioral data. Major privacy work and browser security standards shape how tracking is mitigated, but mitigation is never perfect. Browsers may separate or limit third-party cookies, yet first-party tracking, fingerprinting, and link decoration (parameters in URLs) can still provide useful correlation for ad-tech and analytics intermediaries.
Industry and standards work across the web ecosystem (including W3C discussions around privacy and security properties, and browser vendors’ tracking prevention models) informs how protection mechanisms behave in practice. The key point isn’t “which organization said what,” but rather how the protection layer works on your specific browser and how aggressively a site uses third-party resources.
Practical implication: your search term may be less important than the trackers embedded on the final page and the redirect hops that happen before the final content loads. If the path includes several domains, each hop can introduce additional scripts and data-sharing opportunities.
Some sites use referral funnels: you click from search results, then you’re redirected through intermediate pages designed to do one or more of the following:
These redirect chains make it harder to see what’s truly happening because the intermediate pages can be “invisible” to the average user. From a security perspective, redirect hops also increase the surface area for malicious or privacy-invasive behavior: a user may accept permissions or downloads on a domain that they didn’t intend to visit.
Practical implication: avoid granting notifications, location, or downloads permissions on domains you do not fully trust. If a site starts requesting sensitive permissions early—especially after a redirect chain—treat that as a warning sign.
In higher-risk content categories, ad inventory can be less tightly controlled. That does not mean every ad is malicious, but it increases the probability of encountering ads or embedded frames that attempt to trigger unexpected actions such as:
Reliable sources on general web threats typically emphasize that user interaction patterns matter: unexpected prompts, “urgency” language, and requests to install software or disable protections are common indicators of malvertising. The safest approach is to treat “verification” prompts and “download codec/player” pages as red flags unless you can verify the vendor, the legitimacy, and the download pathway.
Practical implication: if you see unexpected prompts—especially for downloads or “verify you’re human” flows—pause and verify. If you cannot verify, exit the page rather than proceeding.
Some adult-oriented pages, especially those that monetize through pop-ups or fake “support” mechanisms, may include login-like prompts that are not part of a reputable identity provider. A common failure mode is users entering credentials on lookalike pages or “support portals” that mimic real platforms.
Credential theft risk arises from:
Practical implication: use password managers and avoid password reuse across unknown domains. If a login prompt appears in an unexpected place, assume phishing until proven otherwise. Never type credentials into a page you cannot reliably verify.
Another risk pattern is “permission baiting.” A page may be engineered to request browser notifications, camera/microphone access, location access, or file access. Some sites do this immediately; others do it after a user clicks within an overlay. In either case, the permission prompt is a mechanism for:
Permission prompts are not inherently malicious, but their placement and context matter. If a site requests permissions without a clear, user-understandable reason, treat it as suspicious.
Practical implication: refuse or block permissions unless the domain’s purpose is clear and trustworthy. Remember: you can always enable a permission later if you genuinely need it.
Even if third-party cookies are blocked, many sites can still track users using other signals: timing patterns, canvas and WebGL properties, audio fingerprinting, user-agent variants, and aggregated data captured through first-party scripts. Fingerprinting may be difficult to detect without specialized tools. Yet you can still reduce exposure with privacy-preserving settings and by limiting script permissions.
Practical implication: use tracking prevention and limit cross-site data sharing where possible. Additionally, reduce exposure by avoiding pages that require numerous embedded resources, aggressive redirects, or repeated “user interaction” steps that seem unnecessary for the content itself.
Downloads are a major risk lever. When a page asks you to download a “player,” “codec,” or “verification tool,” it may be trying to trick you into installing software that:
Even when the downloaded package is not malware, it may still have privacy-invasive behavior or create persistence on your system.
Practical implication: avoid downloads from untrusted sites. If a browser-native player or well-known media platform suffices, prefer that. If you cannot verify the download’s legitimacy, do not proceed.
Below are practical steps you can take immediately. These steps are general web-safety controls and apply regardless of the specific keyword. Think of this as defense-in-depth: multiple layers that reduce the chance that any single failure results in account compromise or privacy leakage.
Security teams rarely judge risk based on a single keyword. Instead, they assess a multi-factor picture:
Because P0rn0 is often used to obscure search intent or bypass moderation, you may encounter domains that are less transparent. Treat that as a higher-variance browsing environment and rely on your control stack (browser protections plus careful interaction patterns).
In other words: your goal is not to “predict” whether the site is safe. Your goal is to structure your browsing so that if a page behaves badly, the impact is minimized. This is how professionals approach risk in general—especially in contexts where the user cannot fully inspect every moving part.
The table below compares common safety approaches and the conditions required to make them effective. It is not a guarantee; it’s a structured way to think about trade-offs. Many people enable only one mitigation (for example, “adblock”) and assume safety follows. Professionals instead pair multiple controls to cover different threat vectors.
| Approach | What it improves | Conditions/requirements | What to watch for |
|---|---|---|---|
| Tracking prevention + third-party cookie restriction | Reduces cross-site profiling and some ad-tech correlation | Must be enabled in browser settings; keep browser updated | Some sites still fingerprint using first-party data |
| Separate browser profile(s) | Limits cookie and session reuse across browsing contexts | Create dedicated profile; avoid mixing sign-ins | Profiles don’t stop all scripts—still use tracking controls |
| Script/ad filtering (selective) | Blocks many unnecessary third-party resources | Use reputable extensions; review permissions | Over-blocking can break pages; under-blocking reduces protection |
| Permission hygiene (no notifications/location) | Prevents consent-based data collection and spam vectors | Disable prompts or choose “Block”; audit site permissions | Some pages request permissions only after redirects |
| Credential safety practices (password manager + no reuse) | Reduces impact of phishing and credential stuffing | Use unique passwords; enable MFA for important accounts | Some phishing attempts look realistic—verify domain carefully |
For readers seeking authoritative background, consider the following types of sources (examples of reputable, non-exaggerated guidance):
Important: Specific claims about tracking rates or “how often malware appears” vary widely by region, time, and ad network. Professionals avoid hard numbers unless they come from audited reports or well-documented telemetry studies. In safer browsing practice, you should focus on controllable factors: permissions, downloads, domain verification, isolation of sessions, and protection settings that reduce data sharing.
Below is a practical workflow. It’s intentionally conservative—optimized for privacy and security, not for “maximizing access” or minimizing friction. The process also helps you avoid impulsive actions that are common when pages use pressure tactics.
Many users know the general advice (“don’t click suspicious links”), but adults-oriented content discovery sometimes involves unfamiliar sites and aggressive UI. To make the safety approach more usable, it helps to understand specific risk signals you can observe.
If a site requests notifications or location right after the first page load (rather than after you explicitly request a feature), that is a common risk pattern. Legitimate uses usually have a clear user action tied to the permission request (e.g., “Enable notifications for updates”). Permission baiting often attempts to collect consent quickly before you decide.
Some sites use full-screen overlays—“continue,” “watch,” “enable audio,” “verify,” or “allow notifications”—that obscure the content. This makes it easy to click the wrong thing. If you cannot reach content without consenting to something you don’t understand, exit.
Malvertising often mimics legitimate security guidance: “Your browser is blocked, install the secure viewer,” or “Update codec to continue.” Browsers usually warn clearly about dangerous downloads. If a page tries to convince you that you must install something to view ordinary content, treat it as suspicious.
A single redirect can be normal for legitimate tracking or localization, but multiple domain changes—especially through short-lived intermediates—raises the risk profile. You should be alert when the browser’s address bar changes unexpectedly several times after a single click.
Any time a page asks for credentials that aren’t clearly part of a recognized authentication flow, assume phishing. A safe rule is: if you were not expecting to log in to that service at that moment, don’t type anything.
Some scams use “verify you are human” puzzles that demand additional downloads, password entry, or notification permission. Legitimate bot protections exist, but they should not require credential entry or software installation. If verification requires anything beyond a normal CAPTCHA, it’s more suspicious.
Not every user will want to use developer tools, but basic visibility into what’s happening can significantly improve safety. Even without deep technical knowledge, you can use browser features like permissions management, site settings, and extension controls.
Most browsers provide a “Site settings” or “Permissions” panel where you can see which sites are allowed to send notifications, access location, or use camera/microphone. A safer practice is to review these permissions periodically. If you find a suspicious domain granted notification permission, remove it immediately.
Cookies and site data can persist and enable tracking across sessions. If you used a dedicated profile, you may keep that profile separated and clear cookies at the end. If you used your main profile, consider clearing cookies for suspicious domains specifically, rather than wiping everything (unless you prefer a full reset).
When possible, watch the address bar carefully and note the domain changes. If you see a “chain” of multiple domains, it’s an indicator that more than one entity is involved in the page delivery. Your best practice is to avoid interacting after it becomes clear the chain is not transparent.
Ad/tracker blockers are often helpful, but they can also create a false sense of security. Review which extensions have access to “all sites.” Ideally, restrict them to trusted browsing sessions and ensure you’re using reputable extensions. If an extension is unmaintained or asks for overly broad permissions, consider replacing it.
Threat actors sometimes rely on redirect infrastructure and deceptive DNS resolutions. While DNS settings are not a silver bullet, using secure DNS services (where available) and ensuring encrypted connections can reduce the chance of certain interception-style attacks.
Compartmentalization is a concept used in security engineering: isolate risk so that compromise is contained. For everyday browsing, you can apply the same idea with browser profiles.
Create a separate profile specifically for activities that you consider higher risk. Configure it with stricter privacy settings, do not sign into personal accounts, and clear cookies at the end of sessions. This reduces the risk that any tracking session correlates with your main identity.
Some browsers and security tools support containerization or per-tab isolation. The concept is similar: keep cookies and storage separate. This can prevent third-party tracking from tying your browsing behaviors together across contexts.
For users with a high threat model, a dedicated device or user account can provide stronger isolation. This is not always practical, but it’s worth noting because it’s a common professional approach: reduce the amount of personal data stored where you browse high-risk content.
Another practical strategy is to use sessions that you keep short, then close and clear site data. If your browsing profile doesn’t persist cookies long-term, tracking opportunities diminish.
Even careful users can have mistakes: they click “allow notifications,” they download something they shouldn’t have, or they type credentials on a suspicious page. The safest response is structured: contain, assess, then remediate.
Immediately revoke notification permissions in your browser’s site settings. If the site continues spamming through browser notifications, remove the permission and block the domain. Also check for browser-level “push notifications” entries and disable any suspicious ones.
Stop using the downloaded file. Run a reputable antivirus/malware scan, check for newly installed programs, and review startup tasks. If you suspect credential compromise, change passwords for accounts you use in that browser profile (and ideally do so from a trusted device).
Assume compromise. Change passwords immediately on a trusted device and account portal. Enable multi-factor authentication (MFA) on critical accounts. If you used a password manager, also check whether it auto-filled credentials in that context—some managers can indicate which entries were used.
Clear cookies for suspicious domains, revoke site permissions, and review browser privacy settings. If you used a dedicated profile, the impact is likely contained. If you used your main profile, consider clearing cookies and checking account activity logs for anomalies.
Legal requirements depend on jurisdiction and the nature of the content. Many regions impose rules around age verification, consumer protection, and consent for data processing. Additionally, your organization (work/school) may have policies regarding acceptable use and monitoring.
Practical advice: if you are browsing through a managed network (employer, school, or shared device), follow applicable rules. Avoid creating logs that violate organizational policy. If uncertain, use personal devices and ensure compliance with local law.
This article is about security and privacy risk reduction; it is not legal advice. If you need legal clarity, consult a qualified professional in your jurisdiction.
P0rn0 is an obfuscated spelling of a widely recognized adult-related term. People use this obfuscation to reduce keyword-based filtering or bypass moderation triggers. The key takeaway is that obfuscated terms often correlate with higher-risk browsing environments—more intrusive advertising, more redirect activity, and more third-party scripting.
No. A keyword alone cannot reliably determine legitimacy. However, certain keyword patterns can be correlated with traffic sources and page designs that are more likely to include intrusive tracking, redirects, unsafe ads, or permission baiting. Safety is about the site’s behavior and your protections—not the spelling of the keyword.
They significantly help, but they are not a complete solution. Industry practice treats privacy settings as one layer in defense-in-depth, paired with interaction hygiene (permissions hygiene, avoiding downloads, refusing credential entry on untrusted domains) and compartmentalization (separate profiles for higher-risk browsing).
If you allowed notifications, revoke permissions in your browser’s site settings immediately. Remove suspicious domains and consider blocking them via your browser’s content settings. If you downloaded something, stop using it, run a malware scan, check for unwanted software changes, and review account security—especially if you entered credentials anywhere suspicious.
Look for unexpected URL changes after clicking a result, short-lived intermediate domains, and multiple address bar transitions before the final content appears. You can also use browser tools (like network monitoring or developer tools) to observe request patterns if you’re comfortable with that level of inspection.
Legal requirements depend on jurisdiction and the type of content. Many regions impose rules around age verification, consumer protection, and consent for data processing. If you’re browsing through work or school networks, additional policies may apply. When in doubt, follow organizational guidelines and local law.
Professionals typically recommend a combination of: privacy protections, separate profiles, refusing unnecessary permissions, avoiding downloads, and never entering credentials on unverified domains. This approach reduces both privacy exposure and the chance that scams succeed.
Keywords like P0rn0 may appear in everyday search behavior, but the safer path is to treat the surrounding web environment as a high-variance risk zone. With proper browser hardening, permission hygiene, compartmentalized browsing, and a “verify before you interact” mindset, you can substantially reduce privacy exposure and minimize the chance of malicious prompts.
If you want to tailor this into a more specific, non-controversial security setup, share your platform (Windows/macOS/iOS/Android) and browser (Chrome/Firefox/Safari/Brave). A security-focused checklist can be mapped to your browser’s exact privacy settings, permission controls, and session management options—always keeping the emphasis on privacy, safety, and risk reduction.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Explore the Tranquil Bliss of Idyllic Rural Retreats
How to Make Lasting Memories at Disneyland Attractions
Affordable Phones and Plans for Seniors
Affordable Full Mouth Dental Implants Near You
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Discovering Springdale Estates
Unveiling RS Sul Telecom Services
The Guide to Car Trading
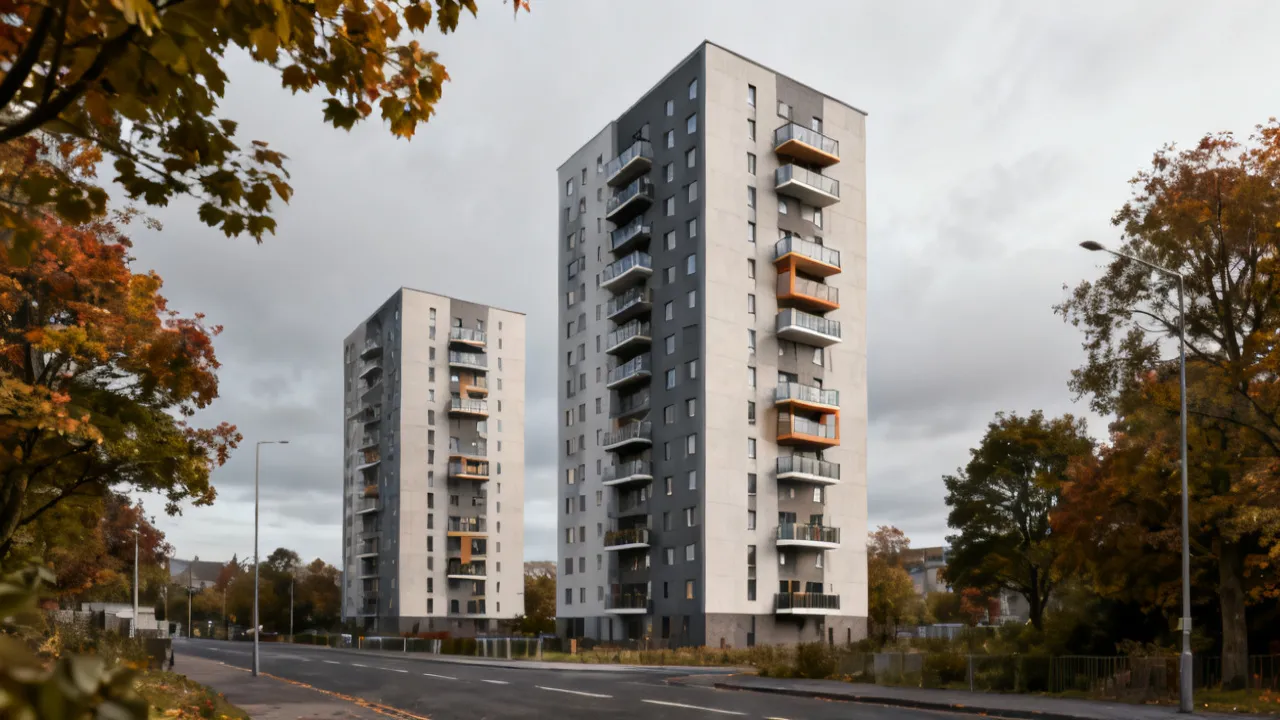
Understanding Londonderry Towers: Location, Value, and Options
This guide explains what Londonderry Towers represents in the local property landscape and how to evaluate living there with a practical, expert lens. Objectively, it discusses how towers influence rental demand, day-to-day convenience, and resale considerations, while outlining the questions tenants and buyers should ask. It also includes conditions, a comparison table, and FAQs to support informed decisions.
Understanding Pinto Aminadabes and Contact-Based Sourcing
This guide explains how to evaluate contact-led sourcing practices, including Pinto Aminadabes and the email address [email protected], with a disciplined, objective approach. It reviews background context on how supplier communication, documentation, and procurement controls affect reliability, response quality, and downstream risk.
Ade Sara: Objective Guide for Buyers and Users
This guide explains how to evaluate Ade Sara carefully, from purpose and sourcing to quality checks and decision criteria. It provides objective background on what “Ade Sara” refers to in the market, common buyer concerns, and practical expectations for supplier verification, labeling review, and product compatibility.
Understanding Mckenna 1993: Context, Methods, and Use
This guide explains the academic and practical context behind “Mckenna 1993,” clarifying how the term is commonly referenced and what researchers typically look for when citing it. Objectively, “Mckenna 1993” is an identifier used in scholarly writing to point to a specific 1993 publication. Background notes cover why citation discipline, methodology clarity, and verification matter in research.
Understanding 25373994391 in Supply Chain Procurement
This guide explains how the reference “25373994391” can be used to support procurement, inventory tracking, and supplier coordination. Objectively, it discusses what numeric item identifiers typically represent in logistics systems, how suppliers manage documentation, and what buyers should verify to reduce receiving errors, delays, and reconciliation issues during warehouse operations.
Maju: Objective Guide to Understanding Its Meaning
This guide explains “Maju” in a clear, objective way—covering its common usage, contextual interpretations, and practical considerations for readers who encounter the term in business, culture, and everyday life. “Maju” is a widely recognizable word in multiple contexts, so understanding tone and setting matters for accurate interpretation.